BNB Chain splits asset power across 4 roles while admins hold the key
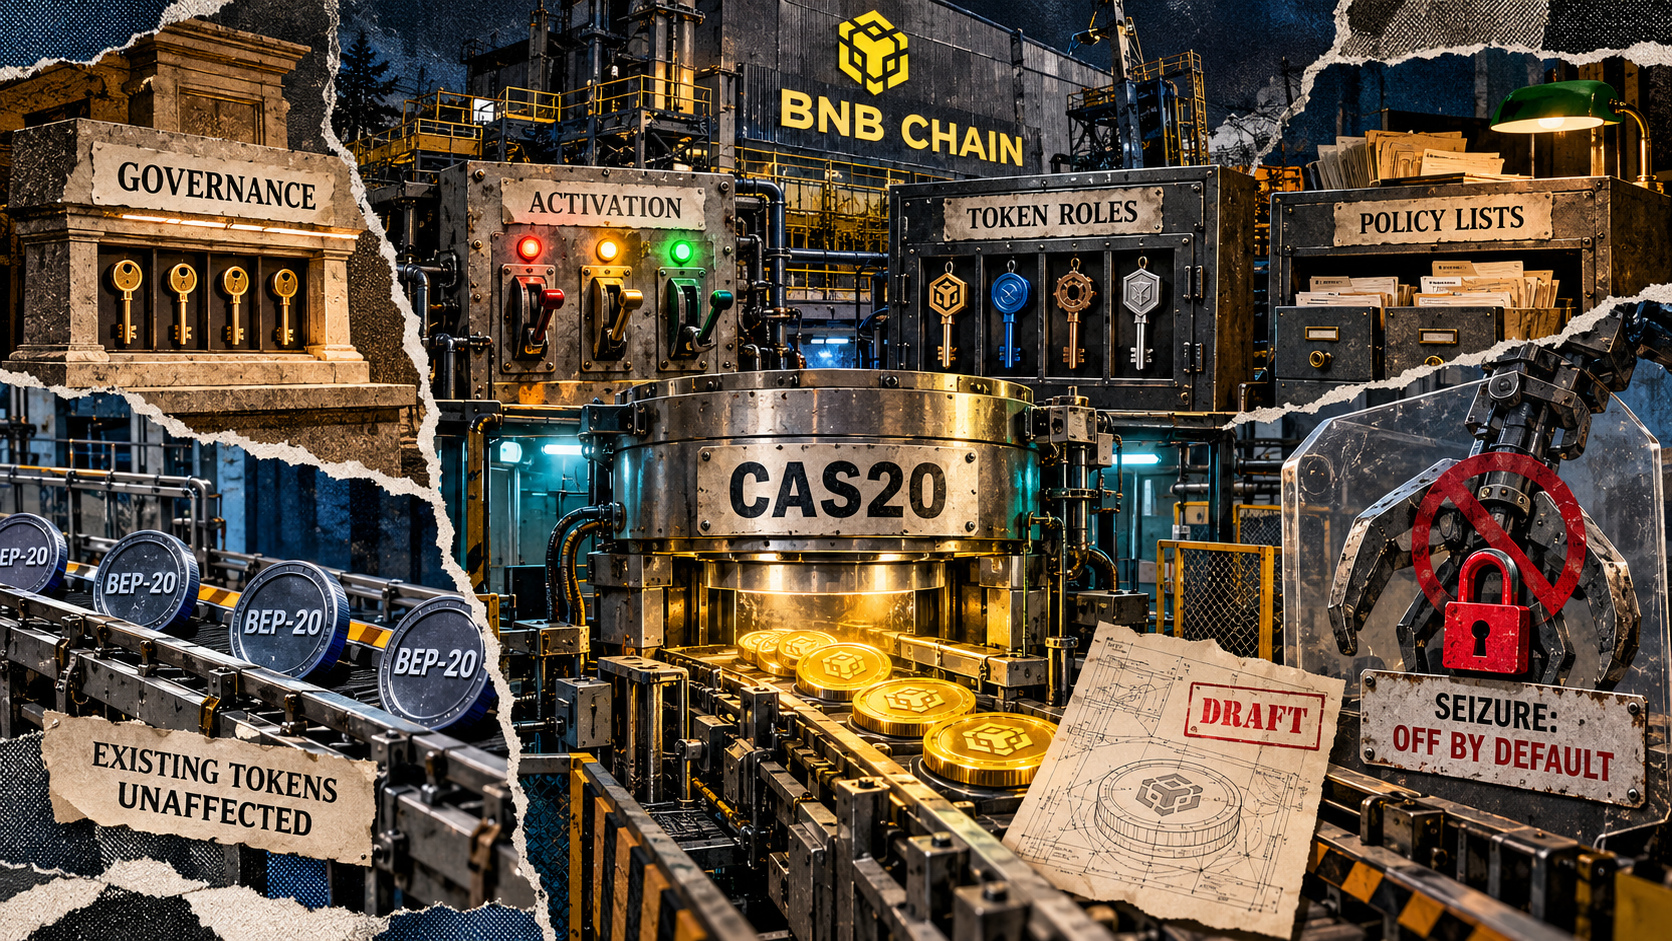

BNB Chain’s Jenner testnet release advances a native-asset design that would give a governance-appointed administrator control over when new stablecoins and tokenized assets can be created.
Issuers could have the code available on the network and still need a separate feature switch opened before launching a CAS20 token.
The Oct. 16 v1.8.1 release schedules Jenner for BNB Smart Chain’s Chapel testnet on Oct. 29 at 02:30 UTC. An earlier announcement gives late-November mainnet guidance, with the exact time still unannounced.
The proposed BEP-702 standard remains labeled Draft and covers the new CAS20 token family, while existing BEP-20 tokens would remain unaffected. Its architecture separates three questions: whether the network admits a feature, who can exercise a token’s powers, and which holders those powers may affect.
CAS20 would put common token behavior into native chain logic, implemented as stateful precompiles. The same design gives network governance a role in making the infrastructure available, alongside the issuer’s control over the asset itself.
Governance would control the opening
Under BEP-702, chain governance appoints the activation administrator through GovHub, BSC’s governance forwarding contract. The administrator then makes separate calls to activate or deactivate features.
The release’s activation implementation enforces that division. Only GovHub can change the administrator, and only the stored, nonzero administrator can operate the switches.
The design provides separate switches for creating Asset-variant tokens, creating Stablecoin-variant tokens, and writing to the shared policy registry.
Once a variant is enabled, the factory’s creation path does not contain an individual-issuer approval list. The creator supplies the initial token administrator and initialization instructions. BNB Chain’s issuer-facing early-access whitelist should not be read as proof that this code licenses each issuer separately.
Closing a token-creation feature would stop new CAS20 tokens of that variant from being created. It would not stop an existing token from minting additional units under its own permissions, transferring balances, or administering its roles.
For an issuer planning a launch, the dependency is concrete: installing Jenner support and activating creation for the chosen native-token variant are different milestones. For an existing holder, the same switch is not a direct mechanism for moving or freezing a balance.
The shared policy registry creates a second dependency after a token exists. A token administrator selects policies for specific operations, and each policy has its own administrator responsible for membership.
The tagged policy implementation gates registry writes behind feature activation, including list membership changes and administrator handovers. A token can keep consulting an existing list even when that list cannot be updated.
Consider an account already blocked by a policy used for transfers. If the policy-registry feature is disabled, the list administrator cannot remove the account while that gate is closed. The holder could remain restricted under the existing rule even though the network-level action did not freeze the token or alter its balances.
The token’s default administrator can still bind another existing policy, because token-level policy binding is outside the registry-write switch. That is different from editing the frozen shared list, and it depends on the token’s remaining administrative permissions.
Reusing one list may simplify operations across several assets, but it concentrates the effect of a membership decision. A change to a shared policy can alter the same account’s eligibility across every token and operation that references it.
Replacing the network’s activation administrator would restore control of the switch, but it would not by itself correct a list entry. Reopening policy writes and updating permitted membership are separate actions.
Issuer permissions govern transfers and seizure
Within a token, role administration and policy selection grant different powers. Minting, self-burning, seizure, pausing and unpausing use separate roles.
You can assign the powers to different addresses or concentrate them in the same one. Network activation authority, token role membership, and policy-list administration remain distinct permissions even if an organization holds several of them.
The ordinary transfer implementation checks the sender and receiver against their respective policies, and checks a delegated executor when it moves another account’s funds.
Minting has a separate recipient policy, so permission to receive newly minted units does not automatically answer whether an account may send tokens or act for another holder.
Seizure would let an authorized operator reassign eligible balances without the holder’s allowance. But its default configuration protects every holder: granting a seizure role alone does not make balances eligible.
The v1.8.1 administrative code calls the holder rule SEIZE_EXEMPT_POLICY. Authorization under it protects the account from seizure. In ordinary calls after creation, reassignment requires the holder to fail that exemption check, plus the token’s seizure role, an unpaused seizure function, sufficient balance, and a valid destination allowed by the seizure-receiver policy.
When those guards pass, seizeWithMemo bypasses ordinary transfer-policy checks and leaves total supply unchanged. Burning instead destroys supply and, for ordinary CAS20 calls, takes only the caller’s own tokens under a separate role.
Transfer restrictions and seizure eligibility consequently cannot be treated as interchangeable. An account’s ability to make an ordinary transfer does not settle whether it could be subject to administrative reassignment.
Pausing transfers also does not pause seizure, which has its own pause setting and still requires its other safeguards.
Base’s Cobalt controls use a similar separation of roles and eligibility on its B20 standard. CAS20’s relevant additional question here is how BNB Chain’s own network-level feature admission would interact with those token-level controls.
The next BNB Chain milestones are operational
BNB Chain’s CAS20 page is seeking early-access issuers and describes Stablecoin and Asset variants.
The governance arrangement also leaves a trade-off for issuers adopting native logic. Common code reduces the need to implement the same token behavior separately, while the proposal warns that a native-client defect could affect multiple CAS20 tokens and require another hard fork to fix.
The Oct. 29 testnet fork is the next scheduled step in the release. A mainnet release date alone would still leave separate questions about which address holds the activation role, how it signs changes, and which features have been opened.
New-token launches would depend on feature admission, ongoing shared-list maintenance would depend on registry availability, and holders’ transfer or seizure exposure would depend on the permissions and policies their issuer actually configures.


